AI cybersecurity: how AI in cybersecurity helps attackers and defenders
AI cybersecurity covers two things: criminals using AI to attack your company, and the use of AI in cybersecurity tools that stop them. Statistics Canada found that scams and fraud were the most common method in cyber security incidents at Canadian businesses in 2023, and AI now makes the emails, phone calls and payment requests behind them harder to spot. You can start defending against them this month with a few written rules and tools you may already pay for. This guide covers both sides, using guidance from the Canadian Centre for Cyber Security.

What AI cybersecurity means
AI cybersecurity, also called AI in cybersecurity, has two meanings. The first is AI as the attacker's tool: software that writes phishing emails, imitates a voice or finds weak points in your systems. The second is AI as a defence: security software that learns what normal activity looks like on your computers and stops what does not fit.
The US National Institute of Standards and Technology (NIST) draws a similar line in a draft Cyber AI Profile. The preliminary draft is dated December 16, 2025, and names three focus areas: securing AI systems, AI-enabled cyber defence, and thwarting AI-enabled cyberattacks. This guide covers the last two. The first has its own guide on AI security.
Three terms come up throughout. Phishing is a message that pretends to come from someone you trust, so that you click a link, open a file or send money. Vishing is the same trick by phone. A deepfake is audio or video generated by AI to look or sound like a real person.
How criminals use AI against smaller companies
The Canadian Centre for Cyber Security (the Cyber Centre) published a statement on AI and cyber security on June 24, 2026. It says threat actors already use AI for phishing, voice scams and deepfake impersonation. The attacks are more convincing, faster and at greater scale. AI also makes it easier for less skilled attackers to carry out sophisticated attacks.
Emails that read like your supplier wrote them
Clumsy grammar used to give phishing away. The Cyber Centre's National Cyber Threat Assessment 2025-2026 says criminals use AI to write personalized phishing emails at scale. The language is correct and mimics human writing styles. The Canadian Anti-Fraud Centre (CAFC) says fraudsters first study a company's language patterns, payment schedules and key contacts. Some register domain names that closely resemble the real company's domain.
Cloned voices and fake video calls
Voice cloning uses AI and a short audio sample to imitate a person's voice, according to the Cyber Centre. The FBI warned in December 2024 that criminals also generate video for real-time chats with fake company executives.
The World Economic Forum reports a case from early 2024 at Arup, a UK engineering firm. An employee sent $25 million to criminals after a video call with deepfakes of senior managers. Rob Greig, Arup's chief information officer, told the Forum that none of the company's systems were compromised. He later tried making a real-time deepfake video impersonating him, using open source software. It took about 45 minutes, and he said the result was not particularly convincing.
The Cyber Centre's social engineering guidance sets the rule: "Audio or video alone should not be considered proof of identity, especially for sensitive or unusual requests."
Invoice and payment redirection fraud
Payment redirection fraud sends your money to a criminal's account by changing the banking details on a real payment. A common version is the CAFC's supplier or contractor swindle: a fake email, made to look like it comes from one of your suppliers, announcing new banking details. The CAFC says these frauds commonly target small and medium enterprises.
The CAFC counts them under spear phishing, meaning phishing aimed at one company or person. Canadians reported $67.9 million in spear phishing losses in 2025, the second-highest dollar loss after investment fraud. Canadians reported nearly $31 million more in the first three months of 2026, the CAFC says.
Faster attacks on exposed systems
AI also speeds up attacks on anything your company exposes to the internet. The Cyber Centre's statement says AI can shorten the time defenders have to respond, in some cases to hours. IBM's 2026 X-Force Threat Index counted a 44% rise in attacks that began with a public-facing application, such as a web portal. IBM ties the rise largely to missing authentication and AI-enabled discovery of weaknesses.
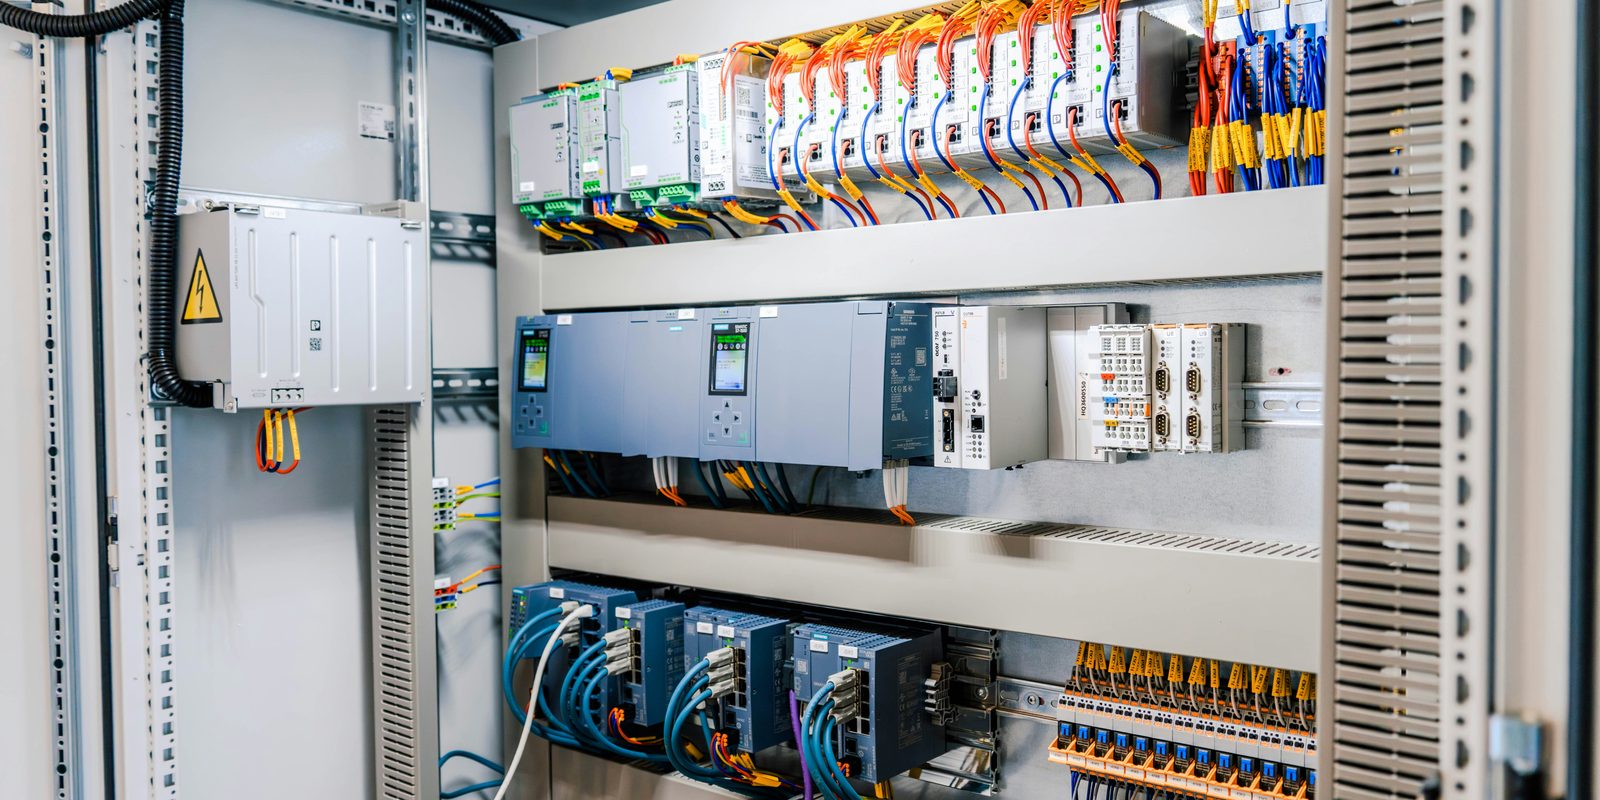
In September 2026, the Cyber Centre warned of a global campaign against programmable logic controllers (PLCs) reachable from the internet. PLCs are small industrial computers that control physical processes such as pumps, valves, pressure and temperature. The attackers use AI to write attack scripts disguised as monitoring software. Critical manufacturing heads the alert's list of targeted sectors, and the alert says attackers target organizations of every size.
What AI has not changed
Most of what AI adds is speed and polish on methods attackers already use. Verizon's 2026 Data Breach Investigations Report found that most AI-assisted malware matched well-known attack techniques. Less than 2.5% of its observations involved less common ones. The UK's National Cyber Security Centre expects AI to raise the volume and impact of intrusions through 2027 by improving existing methods.
Business email compromise (BEC) is email fraud that impersonates an executive or a supplier to get a payment sent. The FBI's 2025 Internet Crime Report lists about US$3.05 billion in BEC losses and says not all BEC tactics are AI-enabled. Businesses reported over US$30 million in losses to BEC scams involving AI.
Cybersecurity for manufacturing: why smaller plants are in scope
Manufacturing topped IBM X-Force's target list for the fifth year, with 27.7% of the incidents it observed. Verizon counted 3,627 manufacturing incidents, 2,713 of them with confirmed data disclosure. Ransomware, malicious software that locks your files and demands payment, appeared in 61% of those breaches.
Attackers got in by exploiting a software weakness in 38% of manufacturing breaches, through phishing in 13%, and with stolen login details in 11%. A third party, such as a supplier or an IT provider, was involved in 61%. Verizon names emails, plans and reports among the favourite items taken.
In Canada, Statistics Canada found that 16% of businesses were affected by a cyber security incident in 2023. Scams and fraud were the most common method. Only 26% had written cyber security policies. The Cyber Centre's ransomware outlook says a ransomware attack can decide whether a small or medium business stays commercially viable.
On the plant floor, the PLC alert says Canada has not had a high-impact incident on industrial control systems so far. It also assesses that the threat is increasing and that future incidents will likely be more severe.
How AI cybersecurity tools work
The Five Eyes cyber security agencies, including Canada's, say AI tools in security work help organizations detect vulnerabilities earlier and respond faster to incidents.
Behaviour-based detection on computers and servers
Older antivirus software matched files against signatures, the fingerprints of malware it had seen before. Behaviour-based tools watch what programs do, such as a process that suddenly encrypts hundreds of files, and stop it. The Cyber Centre's guidance on frontier AI, meaning the most recent and capable AI models, tells organizations to move to behaviour-based anomaly detection.
The product category is endpoint detection and response (EDR), where an endpoint is any computer, laptop or server your staff use. Two examples, as listed on the vendors' own pages on September 26, 2026:
- Microsoft Defender for Business is charged per user per month, paid yearly, for up to 300 users. Microsoft describes AI-powered EDR that disrupts ransomware attacks in progress.
- CrowdStrike includes EDR in Falcon Enterprise, charged per device per year. Its lower tiers, Falcon Go (up to 100 devices) and Falcon Pro, are next-generation antivirus without EDR.
Email filtering
Email filtering reads incoming mail before your staff do and holds back messages that look like phishing. Microsoft 365 Business Premium is charged per user per month, paid yearly, according to Microsoft's page on September 26, 2026. It includes Defender for Business, and Microsoft Defender for Office 365, which Microsoft says protects email from phishing attacks. If you already pay for it, ask whoever runs your IT to confirm both are set up.
Managed detection and response
Managed detection and response (MDR) is a provider that watches your security alerts and acts on them for you. It suits a company with no one on staff to read an alert at night. Choose the provider with care. The Cyber Centre's ransomware outlook says managed service providers (MSPs), the outside firms that run IT for smaller companies, are attractive targets for cybercriminals. The PLC alert suggests writing security responsibilities and liability into service agreements.
What these tools cannot stop
Security software watches systems, and at Arup none of the systems were compromised. The fraud went through a person who believed a video call. The Cyber Centre's top 10 AI security actions list media authenticity checks against deepfakes, alongside out of band verification for sensitive actions. That means a check through a separate channel you already trust.
AI cybersecurity for a $5M to $50M business
Only half of Canadian businesses with 10 or more employees had cyber security employees in 2023, Statistics Canada found. The most common reason for having none was that consultants or contractors monitored cyber security for them (47%). For an owner-led business that makes, moves or sells goods, AI cybersecurity comes down to three decisions:
- Who acts on the alerts. Behaviour-based endpoint tools raise alerts at any hour. Decide whether your IT provider or a managed detection and response service acts on them, and write that duty into the service agreement.
- Which rules are written down. A written payment rule and an AI use policy cover the frauds that go through people, which endpoint tools do not see.
- What your AI tools can reach. If you bought Copilot or ChatGPT licences, or an ERP with AI features, check which files and records each one can read, and under whose permissions. In IBM’s 2026 study, 92% of organizations with an AI-related breach lacked proper AI access controls (global).
The AI security report 2026 has the numbers by business size: how often businesses are hit, what incidents cost and how many organizations have an AI policy.
What to put in place first
Each row pairs an attack on this page with a first control.
| Threat | What it looks like | First control | Source |
|---|---|---|---|
| Payment redirection | A supplier email with new banking details | A call back on a number already on file before any change | CAFC |
| Voice or video impersonation | A call from the owner asking for an urgent transfer | Confirmation on a second, independent channel | Cyber Centre |
| AI-written phishing | A convincing email with a sign-in link | Phishing-resistant multi-factor authentication | Cyber Centre |
| Attacks on exposed systems | A known flaw in a firewall, remote access tool or web portal | Patching internet-facing systems first | Cyber Centre |
| Exposed shop-floor equipment | A PLC reachable through a cellular modem | Confirming nothing on the floor is reachable from the internet | Cyber Centre |
| Ransomware | Locked files and a ransom note | Offline backups and a tested incident plan | Cyber Centre |
A written rule for payment and banking changes
One written rule answers invoice fraud, cloned voices and deepfake calls, and it needs no software. The CAFC recommends detailed payment procedures, including verbal authentication for urgent requests or changes to payment details. The Cyber Centre says to confirm sensitive requests through a second, independent form of communication.
Here is a payment rule a 30-person company could adopt. No change to a supplier's banking details takes effect until someone calls the supplier on a number already in your files. The number in the email never counts. Any transfer above an amount you set needs a second approver. An urgent request from an executive gets a call back on their known number before money moves.
Phishing-resistant multi-factor authentication
Multi-factor authentication (MFA) asks for a second proof beyond the password at sign-in. Phishing-resistant MFA uses a method that a fake sign-in page cannot capture and reuse, such as a hardware security key or a passkey (a sign-in stored on your phone or computer in place of a password). A code sent by text message can be phished, because a person can be tricked into typing it into a fake page.
The Cyber Centre recommends phishing-resistant MFA for all accounts. Its baseline controls for small and medium organizations require two-factor authentication for financial accounts, system administrators and senior executives. The CAFC adds MFA on business email accounts.
Faster patching, starting with what faces the internet
Turn on automatic updates wherever you can. When updates arrive faster than your team can install them, the Cyber Centre's frontier AI guidance says to patch externally exposed and edge-facing systems first. These are the systems reachable from the internet, such as a firewall, a VPN (the secure connection staff use to reach the office network from outside) or a remote access tool. The guidance also says to decommission software and devices that the vendor no longer supports.
Check what on the shop floor the internet can reach
The PLC alert warns that a cellular modem or vendor remote access connection installed during commissioning or maintenance may provide access. Such connections are often undocumented and kept after they are no longer needed. Ask your integrator and machine vendors to list every remote connection into the plant, and remove the ones nobody uses.
Then register for the National Cyber Threat Notification System (NCTNS), a free Cyber Centre service for Canadian organizations of any size. It compares threat information with your internet-facing systems and notifies you about vulnerabilities or malware infections it observes.
Offline backups and a one-page incident plan
Keep at least one backup copy offline, where ransomware on your network cannot reach it. The baseline controls suggest storing backups offline at a secure offsite location. Then write a one-page incident plan that says who to call and which systems to shut down, and test it as the Cyber Centre advises.
Staff who know the new tricks
Only 22% of Canadian businesses gave non-IT staff formal cyber security training in 2023, Statistics Canada found. The Cyber Centre's vishing guidance says to train staff and set clear phone-based verification processes. Cover phone and text as well as email. In Verizon's phishing simulations, the median click rate by voice and text message was 40% higher than by email.
An approved AI tool and rules for company files
The Cyber Centre's June 2026 statement closes its list of actions with clear guidance on responsible AI use, including how to handle sensitive information. Staff who paste drawings, prices or customer lists into personal AI accounts create shadow AI. Give them an approved tool, such as one of the ChatGPT alternatives for business, and a written AI policy. For what makes the setup itself safe, see secure AI at work.
An approved AI tool for company files
Tell Derik which AI tools your staff use today and which files go into them. He will tell you what an approved setup on your own data would take.
Start a conversationCertifications customers may ask for
CyberSecure Canada is a certification that aims to raise the cyber security baseline among small and medium enterprises in Canada. Since March 31, 2023, the program has been handled through the Standards Council of Canada, which accredits the bodies that certify companies. Certification is now against CAN/DGSI 104:2021 / Rev 1:2024, per a 2025 SCC bulletin. The Cyber Centre's Learning Hub offers a free course, Course 625: Cyber Security for Small and Medium Organizations.
If you sell into Canadian defence contracts, watch the Canadian Program for Cyber Security Certification (CPCSC). Level 1 covers 13 security requirements and controls, and select defence contracts require it from summer 2026. Level 2 follows from spring 2027. The program backgrounder says Canada's industrial cyber security standards are technically identical to the US controls behind the Cybersecurity Maturity Model Certification (CMMC).
If money or data is gone
This page is not legal advice. Ask a lawyer about your own obligations.
On a fraudulent payment, contact your bank at once, then report to your local police and to the CAFC through Report Cybercrime and Fraud, online or at 1-888-495-8501. On January 13, 2026, timely reporting helped the CAFC and the US Secret Service freeze a $1.7 million transfer. In an April 2026 case, quick reporting helped recover about $3.5 million for a Quebec business. Report a cyber incident to the Cyber Centre as well.
In Ontario, federal privacy law (PIPEDA) covers small businesses too. You must report to the Privacy Commissioner any breach of personal information that poses a real risk of significant harm, and notify the people affected. You must also keep records of all breaches of security safeguards for two years.
In Quebec, the Commission d'accès à l'information treats a cyberattack such as phishing or ransomware as a confidentiality incident. Where there is a risk of serious injury, notify the Commission and the people concerned, and record every incident in your register.
Bill C-8, which received Royal Assent on June 15, 2026, sets cyber security duties for designated operators in finance, telecommunications, energy and transportation. The telecommunications changes took effect at Royal Assent. The Critical Cyber Systems Protection Act comes into force in phases. For where Canada's proposed AI rules stand, see AI governance.
Securing the AI your team uses
The AI tools your own staff use raise separate questions: where your data goes, who can see it and what the model keeps. For those questions, and for prompt injection (hidden instructions in a document or web page that steer an AI tool), see AI security.
How ThriveAI helps
ThriveAI is an AI engineering company in Ottawa that builds private AI systems for manufacturers and distributors in Ontario and Quebec, on their own data. From this page's list, ThriveAI builds the approved AI tool: a private system your staff can use with drawings, prices and customer lists instead of personal AI accounts. The security software and monitoring above are work for your IT provider.
The platform ThriveAI builds on is designed to keep each client's data on its own server in Canada. You choose the model that reads it: one running on that server, or a hosted model, meaning a model run by an AI provider on its own servers. A hosted model is used under a written zero data retention agreement, in which the provider agrees to keep none of your requests after answering. A hosted model may process requests outside Canada. ThriveAI also runs hands-on AI training for your team, on site and on your own documents. Derik Lawlis, the founder, leads every project, and working sessions run on site with your team, in French or English. More on the company is on the About page.